Cyber Intel Snapshot
Our Cyber Intel Snapshot supports threat-informed cybersecurity advisory with passive external intelligence: credential exposure, public-facing assets, vulnerability context, and plausible attack paths for internal validation. A free check introduces the outside view; the executive briefing is a paid advisory engagement.
Paid executive briefing · Discuss fit and scope on a call
Who the Snapshot Supports
Industries that threat actors actively hunt. Is your sector on their list?
Illustrative scenario only. These are fictional example values, not HostBreach findings about a real organization. No compromise or control effectiveness is established.
Free Security Check
Run the same reconnaissance attackers use. See what they see.
Check Your External Exposure
// passive_mode=true | network_access=false
[+] free_scan | [+] no_system_access | [+] instant_results | [!] email_must_match_domain
Outside View:
-[!] Quick preview only. The Executive External Exposure Briefing includes: breach cost analysis, framework relevance review, insurance impact, illustrative attack-path modeling, attack path mapping. This briefing is a paid, executive-level engagement. The call is to confirm fit and scope.
Schedule Executive Briefing Call →// ABOUT.CYBER_RISK_SNAPSHOT
The Cyber Intel Snapshot is adversary-grade reconnaissance that shows you exactly what attackers see when they target your organization. No agents, no network access - passive external intelligence.
We translate external findings into business questions: possible operational disruption, identity risk, insurer discussions, and relevant frameworks to evaluate. External intelligence alone does not establish compliance gaps or loss amounts.
- Breach Cost Analysis - Estimated exposure using IBM's Cost of Data Breach methodology
- Framework Relevance Review - Identifies which frameworks may be relevant to your business
- Insurance Impact Assessment - How findings affect your cyber insurance position
- Illustrative Attack-Path Modeling - 5-phase attack path modeling with explicit assumptions and validation steps
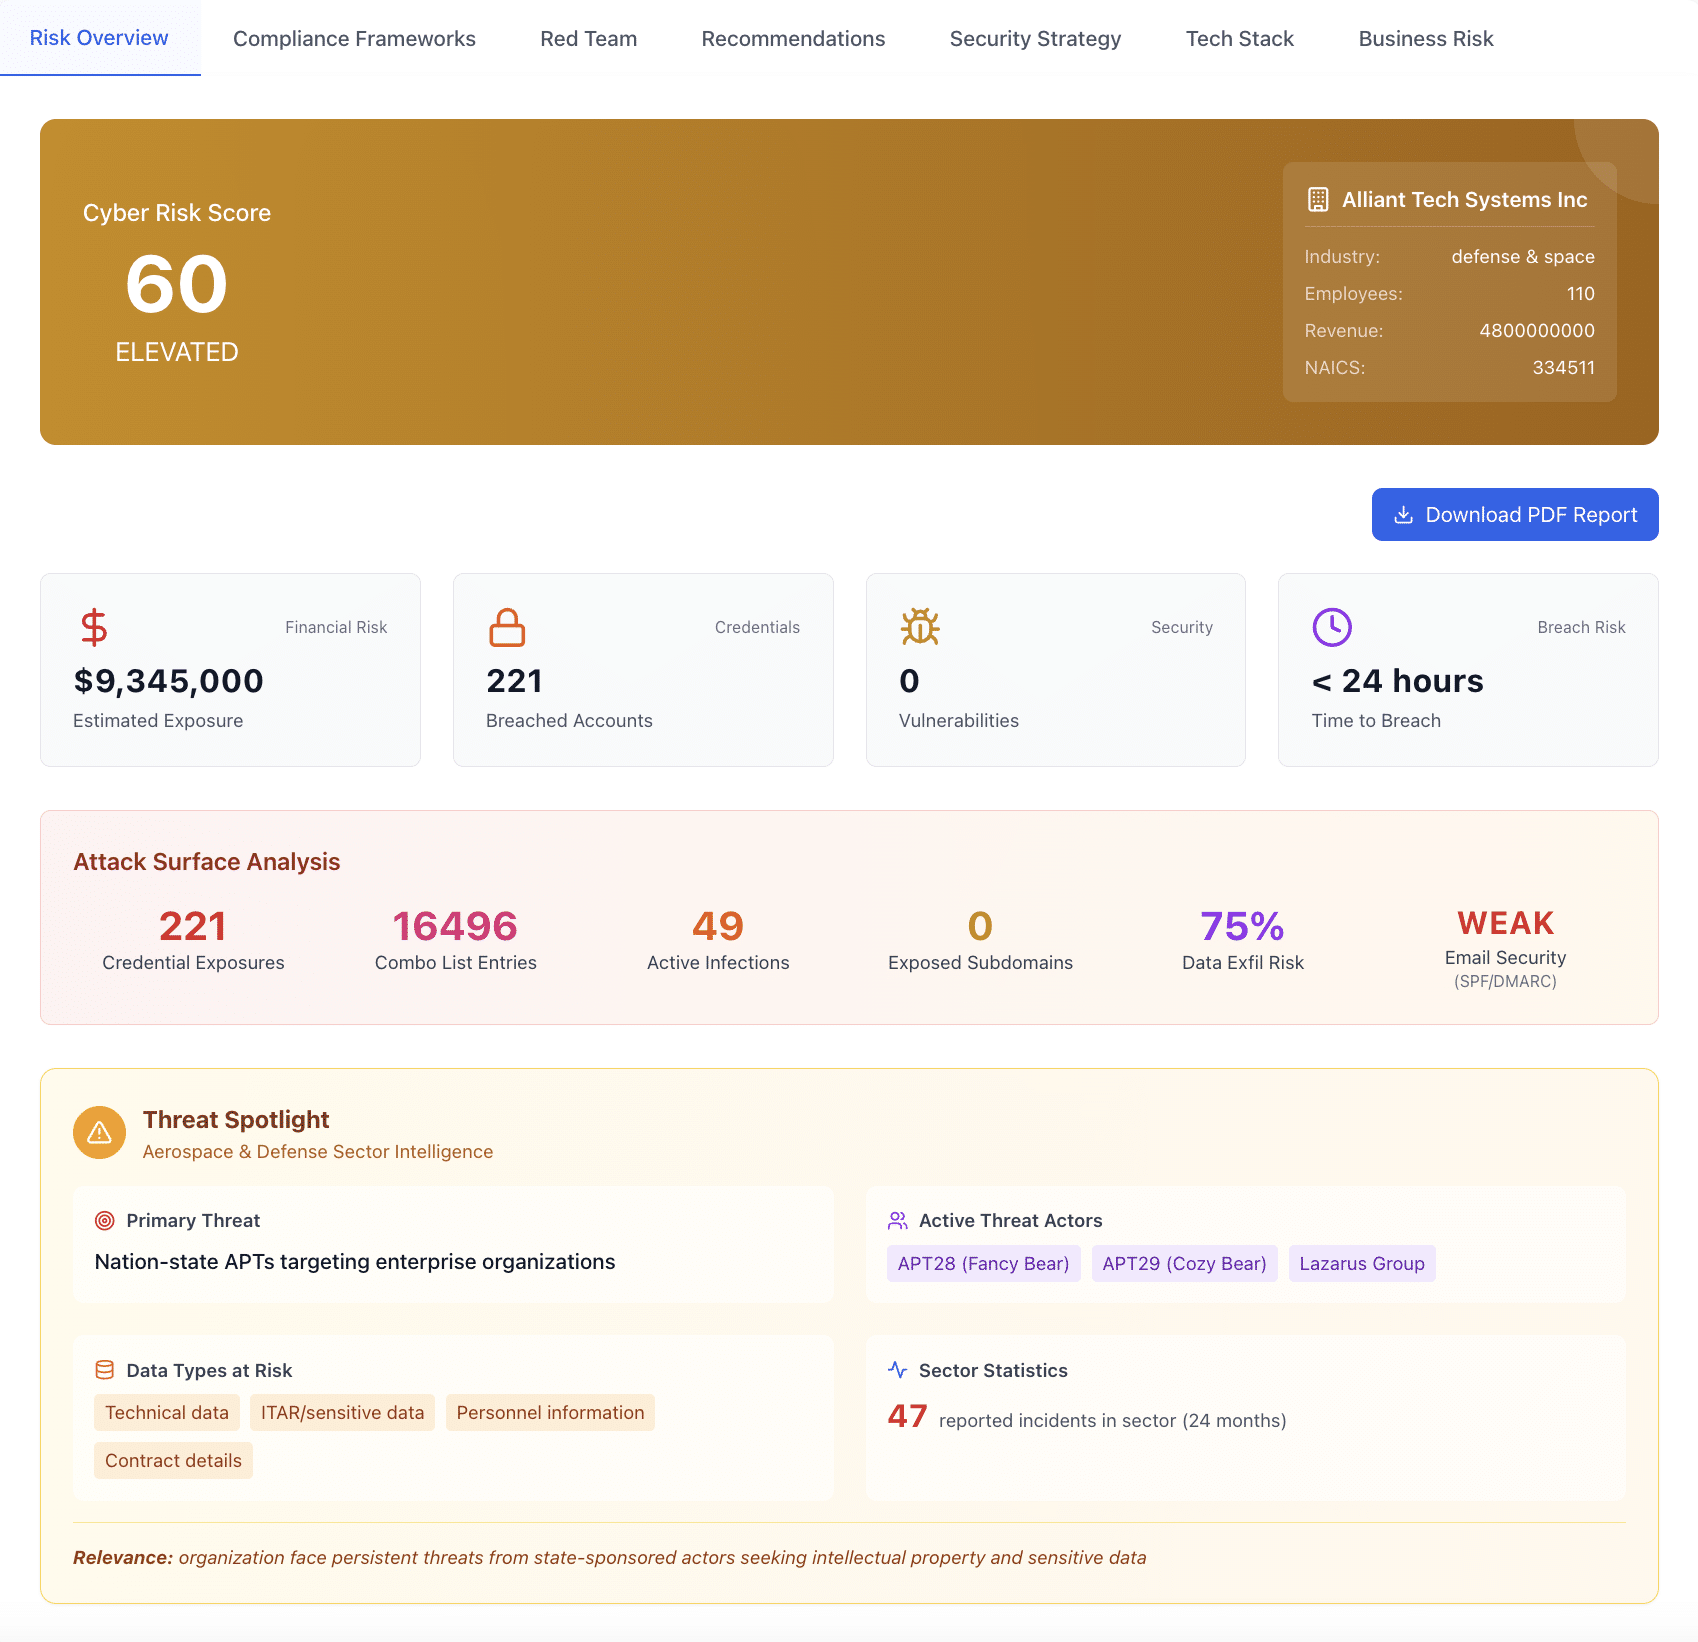
What the Snapshot Covers
What the recon reveals. Technical findings + executive translation.
Breached Credentials & Infostealers
Employee credentials in data breaches and dark web markets. Includes infostealer indicators with session cookies that may enable session hijacking despite MFA.
Identity RiskExternal Attack Surface
Exposed subdomains, development environments, shadow IT, and forgotten infrastructure that attackers use as entry points.
Infrastructure RiskVulnerability Analysis
Externally visible CVEs ranked by EPSS estimates and known-exploitation context, with applicability validated internally.
Technical RiskFramework Relevance Review
Identifies candidate frameworks for review, including those (SOC 2, HIPAA, PCI-DSS, ISO 27001, GDPR, etc.) likely apply based on your industry and business model.
Compliance RiskBreach Cost Analysis
Estimated financial exposure using IBM's methodology. Per-record costs, operational disruption, ransomware recovery estimates.
Financial RiskIllustrative Attack-Path Modeling
Five-phase illustrative attack-path modeling based on external observations. Proposed paths require internal validation and do not demonstrate a successful breach.
Attack SimulationBusiness Impact for Leadership
Security findings translated into metrics your board understands
Context for Better Decisions
Raw data is useless. Context is everything. We show why it matters.
Not This
"You have 523 CVEs and 89 breached credentials"
Raw numbers without context create noise and paralysis. Leadership can't prioritize.
We Deliver This
An illustrative loss scenario connects potential downtime and recovery costs to business assumptions, with a prioritized list of issues to validate.
Business impact with prioritized remediation. Leadership can make decisions.
Not This
"You should consider SOC 2, ISO 27001, HIPAA, PCI-DSS..."
Generic compliance checklists that don't consider your actual business model.
We Deliver This
Your customer base suggests privacy and security frameworks worth reviewing. Applicability requires validation of your contracts, data handling, jurisdiction, and business activities.
Candidate frameworks for review based on industry and business context.
Frameworks to Evaluate
Framework relevance informed by industry and business model; applicability requires internal review
Frequently Asked Questions
Common questions about the recon process
Will this scan touch our network?
No. The Cyber Intel Snapshot is 100% passive OSINT. We only query external intelligence sources - we never scan your systems, install agents, or access your internal network.
How is this different from a vulnerability scan?
Vulnerability scanners probe your systems. We show what's already publicly exposed - breached credentials, dark web mentions, leaked data - things scanners can't see.
What if we're already SOC 2 examined?
Great! We'll show you what attackers see alongside your examination. A SOC 2 report does not establish that every external risk has been eliminated.
Can I share the report with my board?
Yes - that's the point. Reports include executive summaries with business impact metrics, not just technical jargon. Built for leadership consumption.
How accurate is the breach cost estimate?
Loss estimates are planning scenarios, not predictions. Any figures require named sources, dates, explicit assumptions, and internal validation of business inputs. They do not establish insurance coverage or claim eligibility.
Do you sell remediation services?
We're advisory-first. We provide recommendations and can help with compliance readiness, but we're not trying to upsell you managed services or tools.
Plan Your Next Security Decision
See exactly what threat actors see. Before they do. Full briefing is a paid engagement — schedule a call to confirm fit.
Paid executive briefing · Discuss fit and scope on a call
The Cyber Intel Snapshot supports threat-informed cybersecurity advisory and threat-informed vCISO with passive external intelligence. We review credential exposure, public-facing infrastructure, and vulnerability context, then connect observations to business priorities and questions for internal validation. Industry context helps healthcare, financial services, SaaS, and other organizations evaluate relevant frameworks; it does not determine applicability or compliance. Based in Philadelphia, HostBreach provides advisory and risk management for organizations protecting sensitive data.
HostBreach is a threat-informed cybersecurity advisory firm providing CMMC and vCISO services powered by its proprietary Cyber Intel Engine.
External observations require internal validation. They do not independently determine CMMC requirements, scope, compliance, compromise, or insurance coverage.
Threat-Informed CMMC Advisory · Threat-Informed vCISO · Our intelligence layer
DC3 threat reporting · Official CMMC Level 2 assessment guidance